
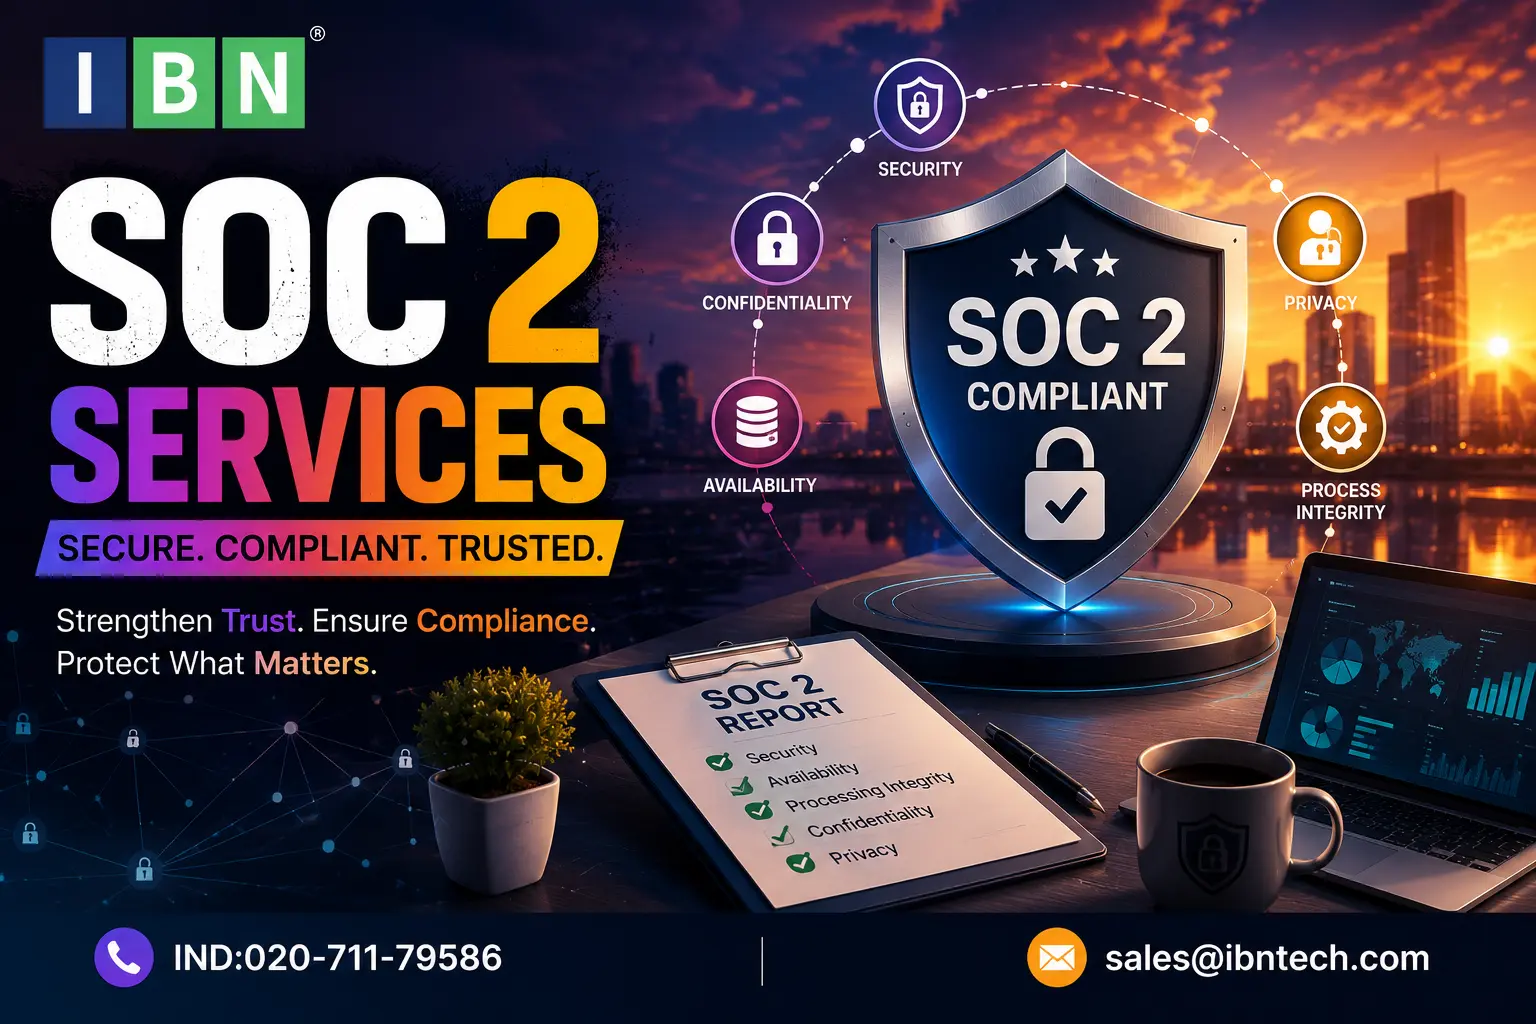
SOC 2 Certification Services for Healthcare Technology and Digital Health Businesses
Why Healthcare Technology Businesses Need Stronger Controls
Healthcare technology companies increasingly manage digital platforms used for patient engagement, telemedicine, healthcare administration, medical workflows, analytics and other technology-enabled services.
The information involved can be highly sensitive, while service interruptions can affect important business and operational processes.
For these businesses, SOC 2 certification services can support the development of structured controls around security, availability, confidentiality and other applicable Trust Services Criteria.
SOC 2 and Healthcare Are Not the Same Compliance Requirement
Healthcare companies should not assume that a SOC 2 report automatically satisfies every healthcare privacy or regulatory requirement.
Different laws, contracts and industry obligations may apply depending on the organisation's operations and the type of information it handles.
SOC 2 should instead be considered one component of a broader security and governance programme.
Access Management in HealthTech
Healthcare applications can involve several categories of users.
Depending on the platform, there may be:
- Internal employees
- Healthcare professionals
- Administrators
- Support teams
- Customers
- System administrators
Each group may require different permissions.
A structured access-management process can help ensure that users receive only the permissions necessary for their roles.
When employees change responsibilities or leave the organisation, access should be modified or removed according to defined procedures.
Protecting Application Availability
A healthcare platform can be difficult to operate effectively when critical systems become unavailable.
This makes availability controls relevant for organisations where system uptime is part of the customer service.
Businesses may need to consider areas such as:
- Backup processes
- Recovery procedures
- Infrastructure monitoring
- Incident response
- Capacity management
- Disaster recovery
- Business continuity
The controls should correspond to the actual services covered by the SOC 2 scope.
Software Changes and Healthcare Applications
HealthTech companies frequently release application improvements and security updates.
A change that appears technically minor can affect customer workflows.
A structured change-management process can help ensure that relevant changes are appropriately reviewed, tested and approved.
This creates traceability between development activity and production systems.
Evidence Makes Controls Demonstrable
SOC 2 preparation is not simply about writing policies.
Suppose a company requires monthly access reviews.
A policy establishes the requirement.
Evidence demonstrates whether the review was completed.
For organisations preparing for Type 2, this distinction becomes particularly important because the operating effectiveness of controls is examined over a period.
The Role of a SOC 2 Compliance Consultant
A SOC 2 compliance consultant can help a HealthTech organisation translate compliance requirements into practical processes.
This can involve:
- Defining examination scope
- Reviewing current controls
- Identifying gaps
- Establishing control owners
- Improving policies
- Planning evidence collection
- Supporting remediation
- Preparing teams for examination
The consultant should understand both the technical environment and the operational context of healthcare technology.
SaaS-Based Healthcare Platforms
Many digital health businesses operate through subscription-based cloud applications.
For these organisations, SOC 2 audit services for SaaS companies may be relevant because application security, cloud infrastructure and software-development controls can form a significant part of the service environment.
However, the examination scope should be determined by the specific service and systems being evaluated.
Third-Party Technology Risks
HealthTech companies may rely on cloud providers, communication platforms, analytics services, hosting environments and other technology vendors.
These dependencies should be considered when establishing a broader control environment.
Vendor management can help organisations identify critical providers, assess relevant risks and maintain appropriate oversight.
Creating a Sustainable Control Environment
The most effective compliance processes are built into normal operations.
Access reviews should be scheduled. Security training should become part of employee lifecycle management. Changes should follow established workflows. Incidents should be recorded and investigated. Recovery procedures should be tested where appropriate.
This makes compliance less dependent on manual preparation immediately before an examination.
Conclusion
For Indian healthcare technology companies, SOC 2 certification services can support stronger security governance and provide structured assurance to customers and business partners.
The focus should remain on building controls that work in the organisation's actual environment.
For HealthTech businesses, sustainable compliance means connecting security, technology, people and operational processes instead of treating SOC 2 as a standalone documentation exercise.
