
SOC as a Service Providers in India: Critical Security Support for SMBs
SOC as a Service Providers: A Security Option for Indian SMBs
Small and mid-sized IT businesses often operate sophisticated technology environments without having the same security resources as larger organizations. Cloud applications, employee endpoints, remote access, business systems, and customer-facing platforms all create security monitoring requirements. soc as a service providers can help these businesses access dedicated security operations capabilities without building every SOC function internally.
For Indian SMBs, the attraction is practical. Security teams need to identify suspicious activity, investigate meaningful alerts, and escalate potential incidents while the business continues serving customers. An external SOC can provide a structured way to support those responsibilities.
Why Managed SOC for SMBs Can Make Sense
A managed SOC provides security monitoring and related operational functions through an external specialist team. Depending on the agreed scope, this may include security-event monitoring, alert analysis, investigation, incident escalation, and reporting.
For organizations considering managed soc for smbs, the value is not simply outsourcing technology. It is gaining an operational security capability that can complement an existing IT team.
An SMB may have capable administrators who understand its infrastructure extremely well, yet those employees may not have the capacity to monitor security events continuously. A managed SOC can address part of that resource gap.
The Security Challenge Facing Smaller IT Businesses
Size does not necessarily make an IT environment simple.
An Indian IT SMB may have employees working remotely, cloud-based applications, development environments, customer systems, corporate endpoints, and third-party technology connections. Each component can introduce security events that require attention.
At the same time, internal teams often have several responsibilities. They may manage infrastructure, user support, applications, cloud services, backups, and technology projects alongside cybersecurity.
Security monitoring can consequently become reactive.
An alert may be reviewed only when someone has time. A suspicious event may compete with an urgent technical issue. Important context may be missed when several systems have to be examined separately.
A dedicated SOC model can provide a more consistent security-monitoring process.
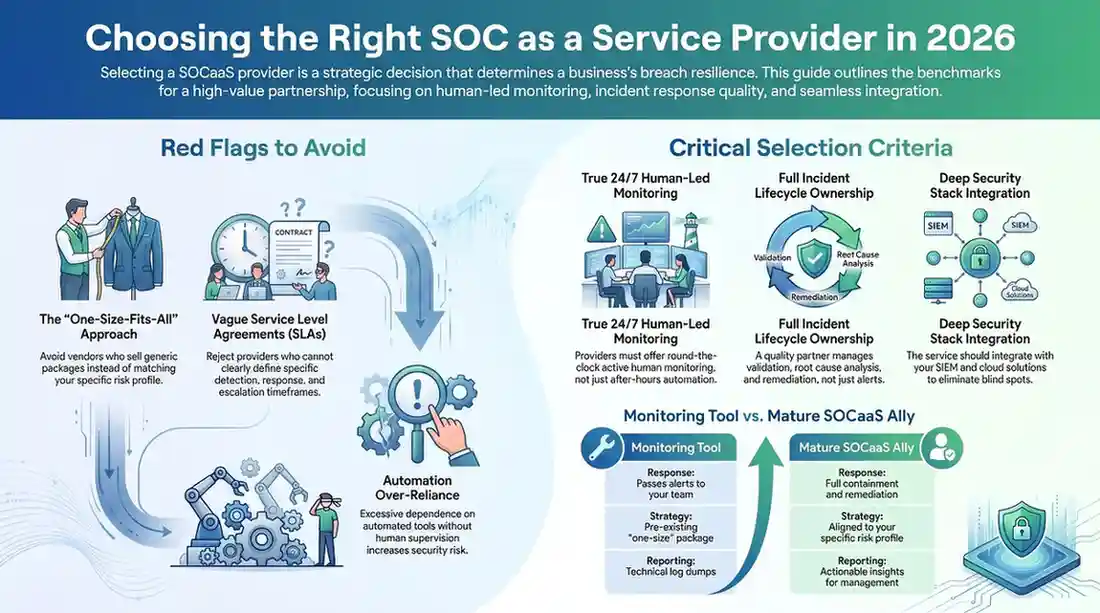
What SOC as a Service Providers Actually Add
soc as a service providers can act as an extension of an organization's security function.
The provider's role should be clearly defined. Monitoring responsibilities, investigation procedures, escalation thresholds, reporting, and customer responsibilities should all be established before the service begins.
This clarity matters because outsourcing security operations does not mean transferring ownership of the business's technology or risk.
The internal organization remains responsible for its systems and business decisions. The provider supplies agreed security expertise and operational support.
Why DIY Security Monitoring Often Becomes Difficult
A business can purchase security technologies without creating an effective monitoring operation.
Security tools can generate useful information, but someone still needs to interpret that information.
Manual monitoring becomes particularly difficult when the same employees are responsible for multiple IT functions. Reviewing alerts may be postponed during busy periods, while unfamiliar events may require more investigation than internal staff can reasonably provide.
There is also the challenge of maintaining consistent procedures.
A structured SOC operation can establish repeatable approaches for alert prioritization, investigation, escalation, and reporting.
That does not make every security incident easy to handle. It does, however, create a defined process for deciding what deserves attention.
How SMBs Should Evaluate a Provider
The right provider should be selected according to the organization's actual security requirements.
Start by identifying the technology assets that matter most. This may include endpoints, network infrastructure, cloud environments, applications, authentication systems, or other business-critical resources.
Next, determine what monitoring is required.
A useful provider assessment should consider:
- Monitoring scope: Which systems and security events will be covered?
- Alert handling: How are events prioritized?
- Investigation: Who examines suspicious activity?
- Escalation: When and how is the customer notified?
- Response: Which actions can the provider perform?
- Reporting: What information will the customer receive?
- Integration: How will the service work with existing security technologies?
- Scalability: Can the service adapt as the business grows?
SMBs should also clarify the boundaries between provider responsibilities and internal IT responsibilities.
A Practical SMB Security Scenario
Imagine an Indian software business where an employee account begins showing unusual access behavior.
The alert itself may not prove that the account has been compromised. There could be a legitimate explanation.
A SOC analyst can review available security information and investigate the surrounding activity. If other indicators suggest that the account may be involved in suspicious behavior, the event can be escalated according to the agreed process.
The internal team can then make informed decisions based on investigated information rather than an isolated notification.
This distinction is important for smaller businesses. Security operations should help reduce uncertainty, not simply add more alerts to an already busy IT environment.
Business Benefits of an External SOC
A managed security operation can provide SMBs with additional security capacity.
Internal IT professionals can continue focusing on technology delivery and infrastructure management while designated security monitoring responsibilities are handled by specialists.
Another potential benefit is consistency. A documented investigation and escalation process reduces dependence on whether a particular employee happens to notice an event.
The model can also provide access to security expertise without requiring the organization to create every specialist role internally.
For a growing business, flexibility can be important as well. New applications, cloud services, users, and infrastructure can change security-monitoring requirements over time.
managed soc for smbs can therefore be useful when a company wants stronger security operations but does not want to build a complete internal SOC immediately.
Common Mistakes When Choosing a Managed SOC
Cost alone should not determine the selection.
A low-cost service may not provide the monitoring scope, investigation capability, or escalation model the business actually needs.
Another mistake is focusing entirely on technology. A security platform is only one part of an operational SOC.
SMBs should ask how analysts investigate alerts and how potential incidents are communicated.
Unclear response responsibilities can create problems during a serious event. The organization should know which actions the provider can take and which require internal authorization.
Businesses should also avoid assuming that compliance is automatically achieved by engaging a SOC. Applicable obligations still need to be identified and addressed through appropriate controls and processes.
Governance and Compliance Considerations
Indian IT businesses may have different security, privacy, contractual, or regulatory requirements depending on their activities, customers, systems, and information-handling practices.
SOC monitoring can support broader governance by providing security-event visibility, investigation activity, and operational reporting.
However, the service should be viewed as one component of an overall security program.
Organizations should identify their specific obligations and determine how monitoring supports their broader security controls, policies, and incident-management processes.
A Practical Managed SOC Checklist
Before engaging a provider, an SMB can review:
- Identify critical systems and business services.
- Define the security events that require monitoring.
- Establish alert-priority criteria.
- Document investigation procedures.
- Set incident escalation thresholds.
- Clarify provider and customer responsibilities.
- Define permitted response actions.
- Establish reporting requirements.
- Review technology integration needs.
- Reassess monitoring as the business environment changes.
Making Security Operations More Accessible
Indian SMBs do not necessarily need to build a large internal security operations department to improve their monitoring capability.
An appropriately structured managed SOC can provide specialist security operations while allowing the internal IT team to retain control over business systems and decisions.
When evaluating soc as a service providers, SMB leaders should look beyond generic claims about monitoring. The meaningful questions concern coverage, investigation, escalation, reporting, integration, and operational fit.
For an Indian IT business, the right external SOC can become a practical extension of its technology team—helping transform security monitoring from an occasional task into a more consistent operational discipline.
Contact Us:
IND- 02067680404
IBN Technologies Ltd.
E-mail: - sales@ibntech.com
