
Security Vulnerability Assessment in India's Energy Sector: Protecting IT and OT Infrastructure
India's energy sector depends on technology for monitoring, management, communication and operational control. Corporate IT, operational technology, remote administration and connected equipment increasingly interact across larger environments. A security vulnerability assessment can help energy organizations understand where security weaknesses exist while keeping availability and operational continuity central to the assessment.
Begin With Operational Criticality
Not every system in an energy environment has the same importance.
An administrative application and an operational control system may both have vulnerabilities, but the consequences of compromise can be very different.
Security teams should therefore classify assets according to their operational role.
Useful questions include:
- Does the system support essential operations?
- Can it be safely taken offline?
- Who can access it?
- What other systems depend on it?
- What happens if it becomes unavailable?
This context improves risk prioritization.
Examine IT-OT Connections
Energy organizations should understand how enterprise systems interact with operational environments.
The security team should identify:
- Network connections
- Remote-access pathways
- Shared authentication
- Administrative accounts
- Data flows
- Third-party connectivity
The objective is not necessarily to eliminate all connectivity. It is to ensure that every connection has a legitimate purpose and appropriate controls.
Remote Administration
Remote access can be operationally necessary.
It can allow engineers and specialists to troubleshoot systems without being physically present.
However, remote access also creates an important security boundary.
Organizations should review authentication, privilege, access duration and monitoring.
Unused remote connections should be removed.
Connected Equipment
Energy environments may include monitoring devices, sensors and specialized infrastructure.
Security teams should maintain visibility into these assets and understand how they communicate.
An asset inventory should be updated when new systems are deployed or old equipment is retired.
Network Security
Network controls are particularly important when multiple operational zones exist.
Security teams should determine whether traffic is appropriately restricted and whether unexpected routes exist between environments.
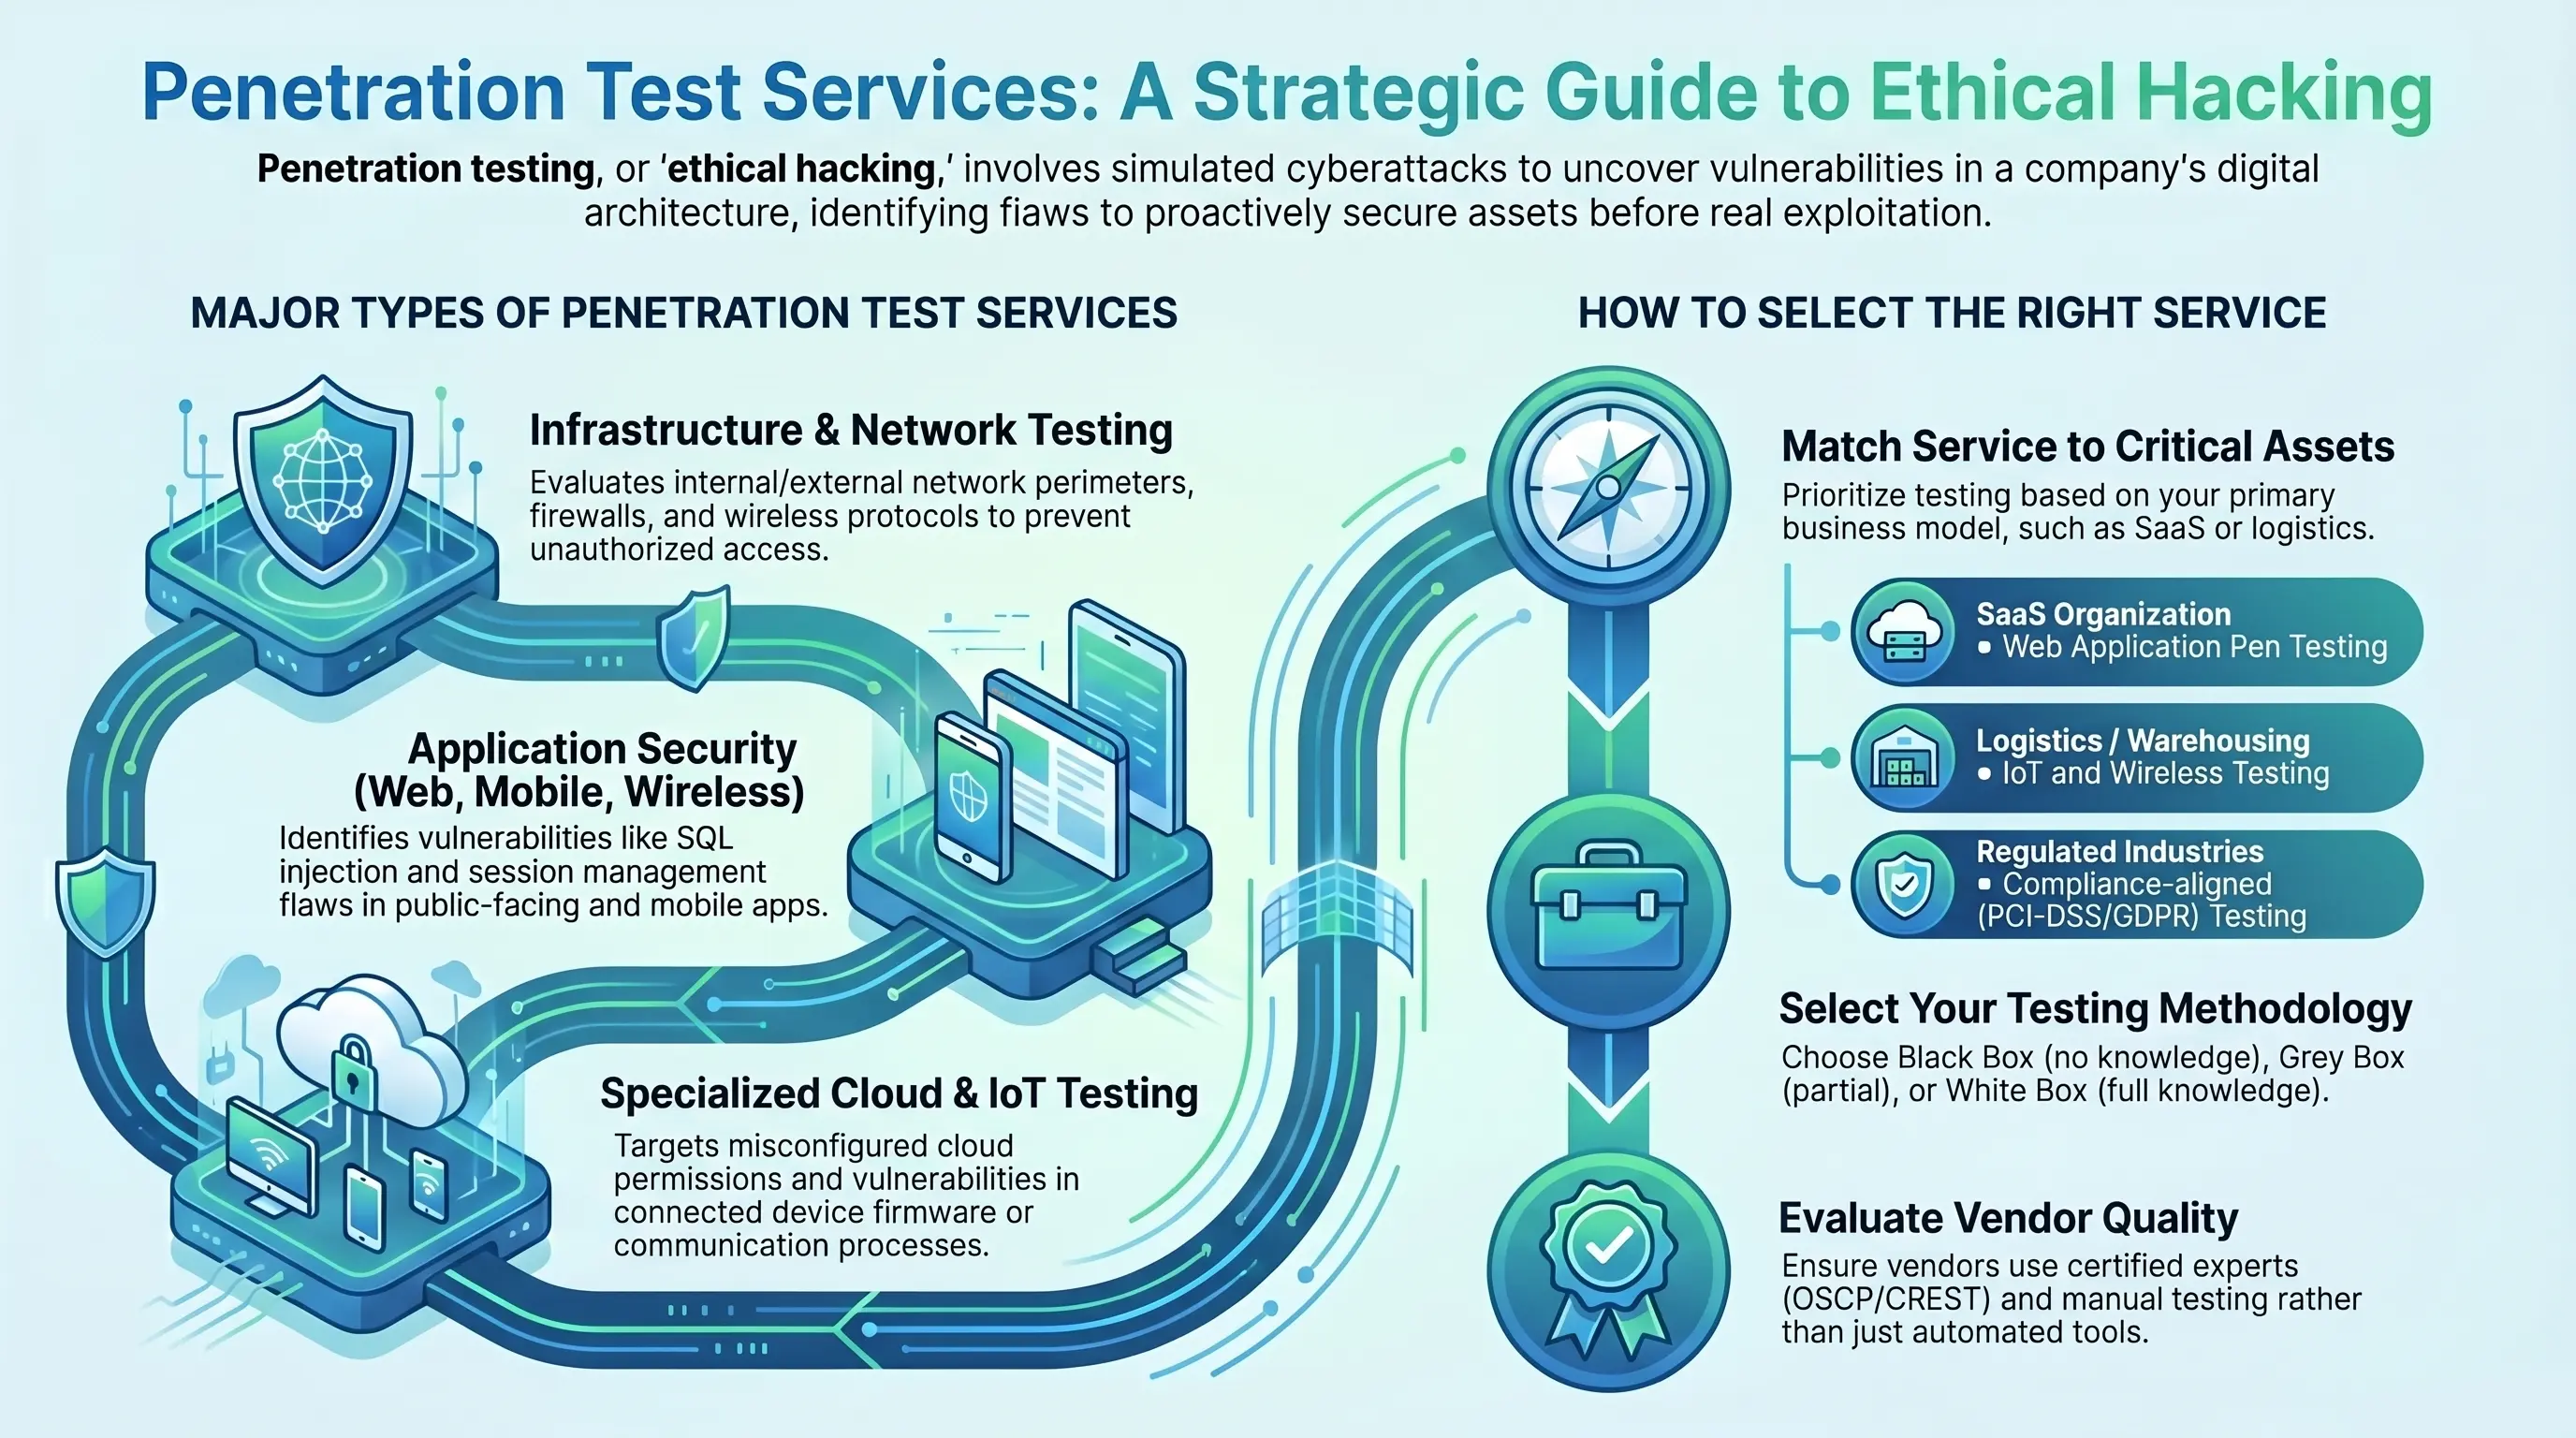
network penetration testing services can be used to validate selected network controls under carefully defined conditions.
Testing should be planned around operational sensitivity and service availability.
Cloud and Enterprise Technology
Cloud platforms may support enterprise applications, analytics and other functions.
Cloud environments should be assessed for excessive permissions, exposed services and weak network configurations.
The relationship between cloud systems and operational networks should also be understood.
Third-Party Access
Energy organizations may depend on equipment vendors and maintenance providers.
External access should be limited to what is required for the specific business purpose.
Security teams should periodically review third-party accounts and remove unnecessary privileges.
What Happens When a Vulnerability Cannot Be Patched?
Operational systems may not always support immediate patching.
In those situations, organizations can evaluate compensating measures such as:
- Network isolation
- Service restriction
- Stronger access controls
- Monitoring
- Removal of unnecessary services
These measures should not become permanent excuses for unresolved vulnerabilities. They should be reviewed until a more durable solution is possible.
Prioritizing Findings
Risk should be considered using both technical and operational factors.
A vulnerability on a system bridging IT and OT may deserve significant attention even if its conventional severity rating does not appear extreme.
The potential consequence matters.
Validate Remediation
After changing network rules, access permissions or remote connections, security teams should verify the outcome.
Retesting helps determine whether the intended protection is actually working.
Strengthening Energy Security in India
As energy infrastructure becomes more digital, cybersecurity needs to be integrated into operational planning.
Asset visibility, vulnerability assessment, network controls, access governance and remediation validation can help energy organizations improve resilience while maintaining the reliability of essential systems.
