
managed soc as a service India: Critical Security Support for IT Teams
Why managed soc as a service Is Becoming a Smarter Choice for Indian IT Businesses
Indian IT businesses operate in environments where applications, cloud infrastructure, endpoints, identities, and business data must remain available while security risks continue to evolve. Maintaining visibility across these environments can become difficult when internal teams are already responsible for technology delivery and operational support.
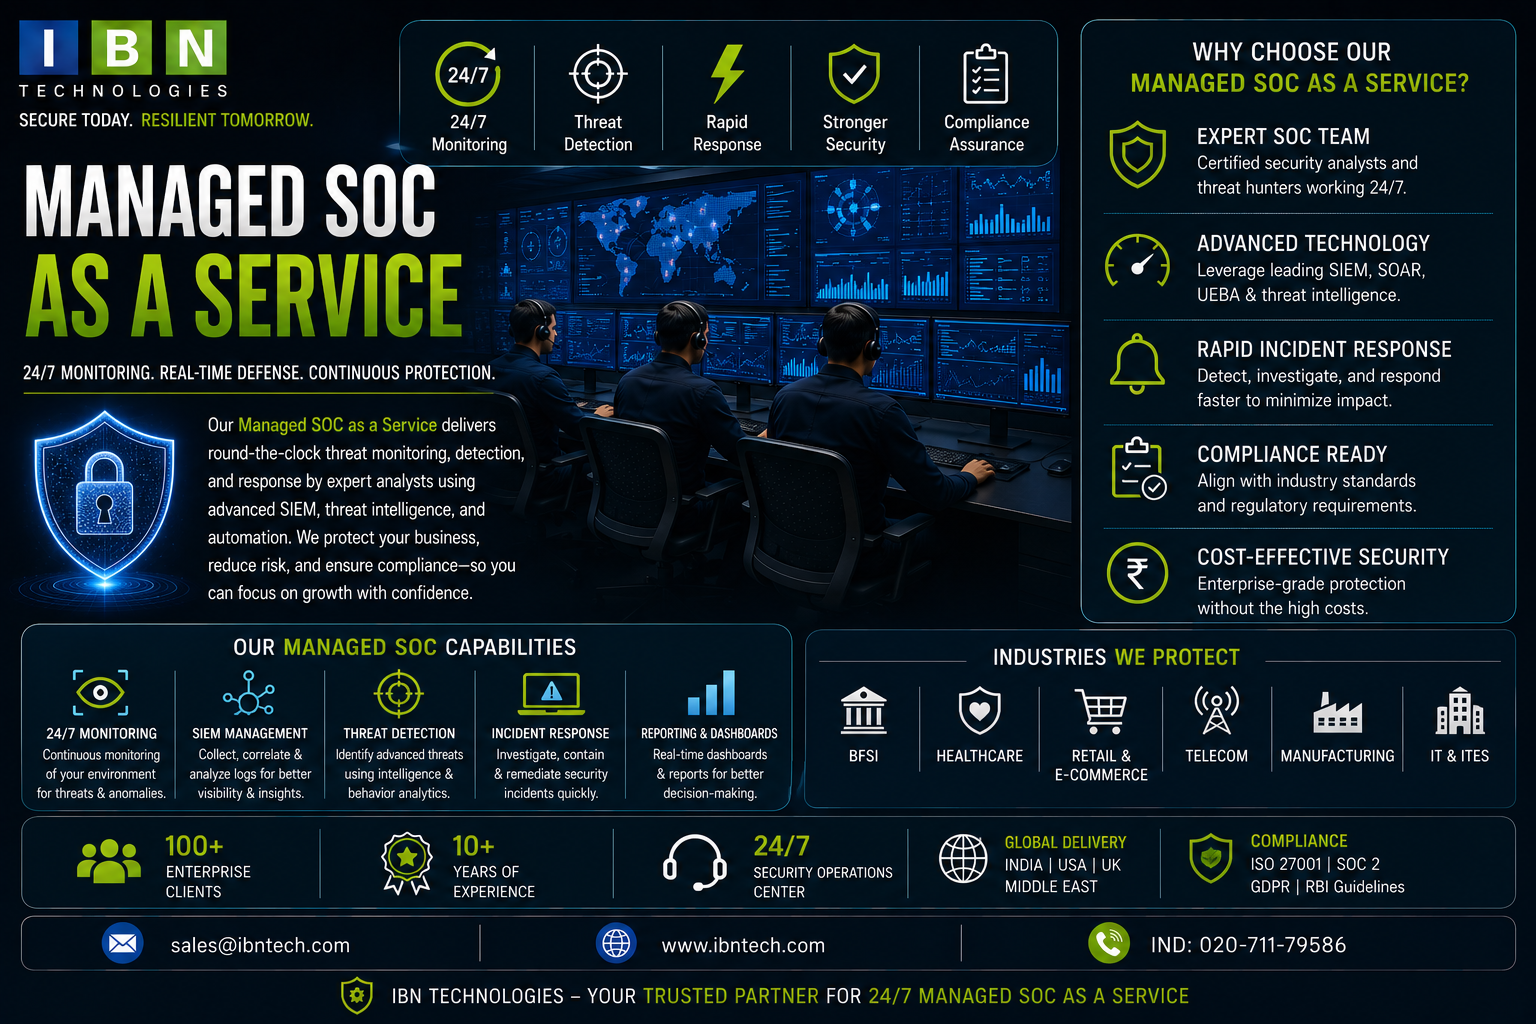
That is where managed soc as a service can provide a practical operating model. It combines external security operations support with structured monitoring, investigation, escalation, and reporting so organizations can strengthen their security capabilities without assuming that every function must be built internally.
For IT organizations, the decision is less about adding another cybersecurity product and more about creating a sustainable way to manage security events.
What Managed SOC as a Service Means for IT Businesses
Managed SOC as a service is an externally supported security operations model in which security specialists help monitor and respond to security events on behalf of an organization.
The objective is to improve security visibility and operational readiness by connecting monitoring, analysis, investigation, and escalation into a coordinated process. It can be particularly relevant when an internal IT team lacks the capacity or specialist resources required for continuous security operations.
The model also allows an organization to define which responsibilities remain internal and which are supported externally.
Why a Managed SIEM Service Can Strengthen Visibility
A managed siem service can help an IT organization centralize relevant security information and support ongoing analysis of events.
Security information becomes more useful when it is interpreted within an operational process. Simply collecting alerts does not guarantee that important events will receive appropriate attention.
A managed approach can help organizations establish clearer processes for reviewing suspicious activity, prioritizing events, escalating significant findings, and communicating security information to relevant stakeholders.
For IT teams, this separation between technology and operational responsibility matters. A SIEM can collect and correlate information, while a security operations function provides the human oversight needed to interpret what those signals may mean.
Where Traditional In-House Security Operations Become Difficult
Building security operations internally can make sense for organizations with the required personnel, processes, technology, and management capacity. However, maintaining those capabilities consistently can be challenging.
IT teams frequently have competing responsibilities. Infrastructure availability, application support, user access, projects, and business requests may all require immediate attention.
Security monitoring introduces another operational demand.
An alert arriving during a period of high workload still needs appropriate evaluation. If the organization lacks clear ownership or sufficient security expertise, investigations may take longer than expected or important context may be missed.
The issue is therefore not simply whether an organization owns security tools. It is whether the operating model can turn security information into timely and consistent decisions.
How the Managed Model Works
A well-defined managed SOC arrangement begins with understanding the organization's technology environment and security priorities.
Monitoring responsibilities can then be established around relevant systems and security signals. Security personnel review events, identify those requiring investigation, and follow defined escalation procedures.
The internal organization remains involved where business context or decision-making is required.
This creates a practical division of responsibility. External security specialists can focus on security operations while internal IT leaders retain visibility into important events and business decisions.
The arrangement should be documented clearly so everyone understands ownership, communication channels, escalation expectations, and reporting requirements.
What IT Leaders Should Evaluate
Choosing a managed SOC model should not be based solely on the promise of continuous monitoring. IT leaders should examine the operating process behind that monitoring.
Important evaluation areas include:
|
Evaluation area |
What to examine |
|
Monitoring coverage |
Which environments and security signals are included |
|
Alert handling |
How events are reviewed and prioritized |
|
Investigation |
How suspicious activity receives deeper analysis |
|
Escalation |
When and how significant findings reach internal teams |
|
Reporting |
Whether security information is communicated clearly |
|
Responsibility |
Which activities remain with the internal organization |
|
Documentation |
Whether operating procedures are clearly defined |
|
Adaptability |
How the service can respond to changing business requirements |
This evaluation helps move the conversation away from technology checklists and toward operational outcomes.
Business Benefits Beyond Alert Monitoring
A managed security operation can provide several practical advantages for IT organizations.
The first is greater operational focus. Internal technology teams can spend more time on business systems and technology priorities while specialist security personnel handle defined monitoring and investigation responsibilities.
Another benefit is process consistency. Security events can follow established workflows rather than depending entirely on whichever employee happens to be available when an alert appears.
The model can also improve management visibility. Structured reporting gives IT leadership a clearer view of important security events, outstanding issues, and areas that require attention.
Most importantly, the service can provide a framework for turning security signals into action.
Why Security Operations Need More Than Technology
Technology provides visibility, but visibility alone does not create security readiness.
A mature security operation requires people who understand how to interpret events, processes that determine what happens next, and communication paths that connect technical findings with business decisions.
This is why managed SOC arrangements should be evaluated as operating services rather than simply as monitoring tools.
A Practical IT Use Case
Consider an Indian IT organization supporting several business applications while maintaining a distributed technology environment.
The internal team may already monitor infrastructure performance and application availability. Security events, however, require a different type of analysis.
Suppose unusual authentication activity appears across an important system. The organization needs to determine whether the activity represents legitimate behavior, an account issue, or a potentially serious security event.
Under a managed SOC model, the security operations function can review the relevant signals and investigate according to established procedures. If the event requires internal action, the appropriate IT or business stakeholder can be engaged.
The value comes from having a defined workflow rather than simply generating another alert.
Getting the Operating Model Right
Organizations considering managed security operations should establish expectations before implementation.
Useful questions include:
- Which environments require monitoring?
- What types of security events require escalation?
- Who owns incident decisions?
- How should urgent findings be communicated?
- What information should regular reports contain?
- Which activities remain the responsibility of internal IT?
- How will changes to the environment be communicated?
- How frequently should the operating arrangement be reviewed?
Clear answers reduce ambiguity and make the relationship easier to manage.
Compliance and Governance Context
Security operations should also support an organization's broader governance responsibilities.
A managed SOC can contribute to operational visibility and security oversight, but organizations should not assume that using an external security service automatically establishes compliance with every applicable requirement.
IT businesses should identify the obligations relevant to their own operations and determine what controls, processes, documentation, and evidence are required.
The managed service can then be aligned with those expectations.
This approach is more reliable than treating cybersecurity operations and compliance as separate activities.
Building a Sustainable Security Capability
Indian IT businesses do not necessarily need to choose between having no security operations capability and building a large internal SOC from the ground up.
A managed model can provide another path: defined external security operations combined with internal ownership of business decisions and technology priorities.
When evaluating managed soc as a service, organizations should focus on how monitoring, investigation, escalation, communication, and reporting work together.
For IT leaders, that practical operating model is ultimately more important than the label attached to the service. A security capability becomes valuable when it consistently helps the organization recognize important events, understand their significance, and respond through an established process.
Contact Us:
IND- 02067680404
IBN Technologies Ltd.
E-mail: - sales@ibntech.com
